
This article seeks to acquaint practitioners with the intricacies of Linux system forensics through the meticulous examination of a compromised Kali Linux evidentiary image attributable to an adversarial actor.
The forensic image under analysis was graciously furnished by Dr. Ali Hadi, having been originally presented and conducted as a hands-on workshop at OSDFCon 2019. The requisite download location is hosted on his official website.
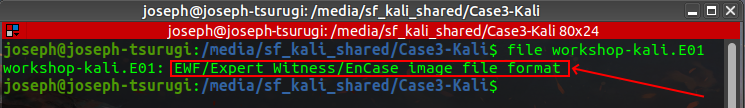
The initial phase of the examination entails the identification of the bitstream image format. To this end, the file utility was invoked against the forensic image. This command performs a comprehensive series of magic-byte signature tests, heuristic evaluations, and content-based analyses to ascertain the precise file type based on its embedded structural signatures. Execution of the file command on the subject image conclusively determined it to be an EWF (Expert Witness Format / EnCase) forensic image.
Prior to commencing the forensic examination, baseline metadata and evidentiary attributes of the subject image were acquired. The stat utility was employed to extract critical filesystem intelligence, including the image’s allocated size, temporal metadata (access, modification, and status change timestamps), inode information, and block allocation details, as illustrated below.

In the context of a Linux-based forensic workstation, evidentiary disk images must typically be presented in raw format for optimal compatibility. Most native Linux utilities and forensic tools expect direct access to a raw bitstream representation. Common forensic image formats—such as E01 (EnCase), AFF, and even split raw images—are not natively consumable by many standard Linux commands and mounting mechanisms.
The initial acquisition step, therefore, involves transforming the subject EWF/E01 image into a raw-accessible view. This is accomplished through the use of ewfmount, a component of the libewf library. The utility creates a virtual raw representation of the forensic image’s contents, exposing it as a mountable block device suitable for subsequent analysis and examination.

Upon successful execution of the ewfmount command, the designated destination directory will contain a virtual raw disk image file that precisely mirrors the original source disk in size. This artifact, invariably named ewf1, is presented as a strictly read-only block device, ensuring the preservation of evidentiary integrity throughout the analysis. The forensic image is now ready for detailed examination using the appropriate Linux forensic tools and methodologies.

The subject system employs a DOS/MBR partitioning scheme, as evidenced by the prior output. Partition 1 constitutes a Linux partition formatted with the Ext4 filesystem, bearing the UUID 2F925E17-7279-45F8-99B6-7EF241EB45E8. This partition is flagged as bootable and encompasses approximately 78 GB of allocated space, corresponding to 163,577,856 sectors. All subsequent forensic analysis will be conducted exclusively on this primary partition. Additional details regarding the disk geometry and partition layout of the attacker’s system may be further elucidated through the fdisk utility.

Further analysis reveals that each sector on the subject disk is 512 bytes in size, with a disk identifier of 0x553B71F4. The partition table resident within the forensic image can also be enumerated to determine the precise starting sector offsets for each partition through the use of the mmls utility (part of The Sleuth Kit). This provides critical insight into the layout and boundaries of the allocated partitions on the attacker’s system.

Leveraging the starting sector offset of Partition 1 (as identified above), detailed filesystem metadata can be interrogated as follows.
The fsstat utility, a core component of The Sleuth Kit, accepts a forensic image (or offset-adjusted raw device) of a specific filesystem and systematically enumerates comprehensive structural intelligence. It furnishes in-depth reporting on filesystem parameters, metadata structures (including inode and block allocation details), content data characteristics, and sector-level layout information, thereby enabling a thorough understanding of the underlying filesystem architecture.

At this juncture, a comprehensive enumeration of the evidentiary artifacts within the subject partition is required, encompassing both active and deleted files and directories.
The fls command, an integral utility within The Sleuth Kit, is employed for this purpose. It systematically traverses the filesystem and reports the names, permissions, ownership attributes, and full MACB (Modified, Accessed, Changed, and Born) timestamps for all entries. Critically, fls recovers and displays information regarding deleted files and directories that have not yet been overwritten, thereby providing essential visibility into potentially relevant artifacts that might otherwise remain concealed.

Advancing the examination, a bodyfile is now generated from the filesystem using the fls utility. This capability represents a powerful forensic construct, enabling the systematic creation of detailed timelines of file system activity — a technique particularly valued by practitioners for reconstructing chronological sequences of events.
Two key command-line switches were incorporated:
- -r — instructs the tool to recursively traverse all directory entries.
- -m — specifies output in the mactime bodyfile format, incorporating the designated mount point for accurate timeline correlation.
This bodyfile serves as the foundational dataset for subsequent timeline analysis of the attacker’s file system.
sudo fls -r -m "/" -o 2048 /mnt/evidence/ewf1 > bodyfile.txt

Utilizing the mactime utility in conjunction with the generated bodyfile, a comprehensive MACB timeline of file system activity on the attacker’s system can now be constructed.
Such timelines represent a powerful and indispensable analytical capability in digital forensic investigations. They are particularly effective in cases involving malware deployment, system compromise, or other adversarial activities, enabling examiners to reconstruct the chronological sequence of events, correlate artifacts across time, and identify patterns of malicious behavior with high precision.
mactime -b bodyfile.txt -d > timeline.csv
The -b option specifies the input bodyfile from which the timeline is to be generated, directing the utility to process the previously created dataset containing the filesystem metadata. The -d flag enables delimited output, producing a comma-separated values (CSV) format that facilitates subsequent import and analysis within spreadsheet applications such as OpenOffice Calc or equivalent tools. This format significantly enhances the examiner’s ability to sort, filter, and pivot large volumes of temporal data. Additionally, the -z switch may be utilized to explicitly define the target timezone, ensuring accurate normalization of all timestamps relative to the appropriate investigative context.

The subsequent phase involves mounting Partition 1, the primary repository of evidentiary data, thereby enabling direct access via standard Linux command-line forensic and system utilities for artifact discovery, recovery, and extraction. This mount operation grants examiners the ability to traverse the Ext4 filesystem using familiar tools such as ls, find, grep, strings, and other specialized utilities, facilitating efficient identification and preservation of relevant digital evidence.

With the successful mount of Partition 1, all files and directories resident on the root volume are now accessible for detailed inspection and processing. By referencing the designated mount point at /mnt/analysis/, I can interact directly with the filesystem hierarchy using native Linux forensic utilities, as illustrated above.
Before proceeding with more granular forensic analysis, the investigative context shall be framed by considering the underlying crime case as resolved, thereby establishing a structured foundation for deeper artifact examination and event reconstruction.

Forensic Analysis Of The Linux Machine
As an initial step in the forensic examination, the practitioner will conduct a comprehensive system enumeration of the suspect machine. Presented below are the pertinent specifics regarding the operating system employed by the attacker.

The next critical objective in the system enumeration is to ascertain the installation date and time of the attacker’s machine. The dumpe2fs utility is employed for this purpose, as it extracts and displays detailed superblock and block group metadata for the target Ext4 filesystem. The process begins with the identification of the device name corresponding to the root (/) partition. Once the appropriate block device is determined, the dumpe2fs command is executed against it to recover the Linux operating system installation timestamp, which is typically embedded within the filesystem’s superblock as the creation time of the root inode or filesystem initialization date.

It is essential for the forensic examiner to establish the default timezone configured on the subject system under investigation. Linux log files, system artifacts, and other time-sensitive evidence typically record timestamps in the machine’s local timezone. Accurate identification and normalization of this timezone are critical to ensure proper temporal alignment and correlation of events throughout the analysis.

With a solid foundational understanding of the subject system’s configuration and baseline characteristics now established, the examination shifts toward the identification and analysis of malicious activity.
Given the context of a suspected web server exploit, the immediate priority is a targeted review of database-related logs. These artifacts are conventionally located within the /var/log/ directory hierarchy. System and application logs in this location frequently contain a wealth of actionable intelligence, including authentication events, query executions, error conditions, and anomalous behavior that can reveal the tactics, techniques, and procedures (TTPs) employed by the adversary.

Given the ubiquity of web server compromises in modern intrusions, forensic examiners can expect to devote a substantial portion of their DFIR engagements to the meticulous scrutiny of web server access, error, and application logs.
These artifacts frequently serve as critical evidentiary sources, revealing the precise temporal window of the breach, the originating IP addresses and geolocations of the adversaries, as well as indicators of the exploit methodology and post-exploitation behavior. Examination of the PostgreSQL database logs disclosed notable network listening activity spanning from 2019-09-06 22:45:23 to 2019-09-30 13:02:53 UTC.

The foregoing log analysis furnishes a definitive response to the initial investigative query. The temporal window of the exploitation activity is precisely delineated as 2019-09-06 22:45:23 through 2019-09-30 13:02:53 UTC.
This determination prompted further inquiry into the inventory of installed applications on the attacker’s system, with particular emphasis on their respective last access timestamps, in order to reconstruct the software ecosystem and identify potentially malicious or post-exploitation tooling.
ls -lt --time=atime /mnt/analysis/var/cache/apt/archives
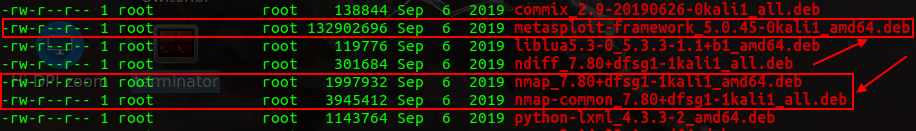
Analysis of the command output revealed a compelling temporal pattern. The majority of installed applications on the subject system exhibited last access timestamps concentrated on September 6 and 7, 2019 — precisely aligning with the established window of the intrusion. Notably, both the NFS server and VNC applications were accessed during this period, as illustrated in the figure below. These findings are highly indicative of attacker activity and merit further scrutiny.

The figure below further discloses that the Metasploit Framework and Nmap were also accessed during the same critical timeframe. These tools, well-known within the offensive security community for reconnaissance, exploitation, and post-exploitation activities, strongly corroborate the presence of deliberate adversarial operations on the compromised system.
A particularly valuable source for identifying installed applications and package management activity on the subject Debian-based system resides in the /var/log/apt/ directory. This location contains historical records of package installations, updates, and removals managed by the Advanced Packaging Tool (APT), offering examiners significant insight into the software ecosystem present on the attacker’s machine.

Examination of the history.log file within the /var/log/apt/ directory disclosed significant post-compromise activity. The following remote access tools were installed after the initial breach:
- tigervnc-viewer
- nfs-server
These packages were installed on 2019-09-07 at 22:48:19, firmly within the established window of the attack. This finding strongly indicates deliberate post-exploitation persistence and remote access mechanisms established by the adversary.

To further operationalize the established temporal window of the attack, the following step translates the identified timeframe into a targeted list of files accessed on the attacker’s system during the period of compromise.
find /mnt/analysis/ -newermt "2019-09-06 22:45:23" -not -newermt "2019-09-30 13:02:53" > /media/sf_kali_shared/accessed.txt
This command leverages the find utility to recursively enumerate all files and directories within the mounted root volume whose access timestamps (-newermt) fall between the start and end of the exploitation window, effectively generating a focused manifest of potentially relevant artifacts for subsequent review. The output is redirected to an accessible file for documentation and analysis.

The listing below highlights additional artifacts consistent with those previously identified, including traces associated with the Metasploit Framework, VNC, FTP, and related tools. Notably, several of these files and directories appear to have been deliberately concealed, suggesting an attempt by the attacker to obfuscate their presence and activities on the compromised system.
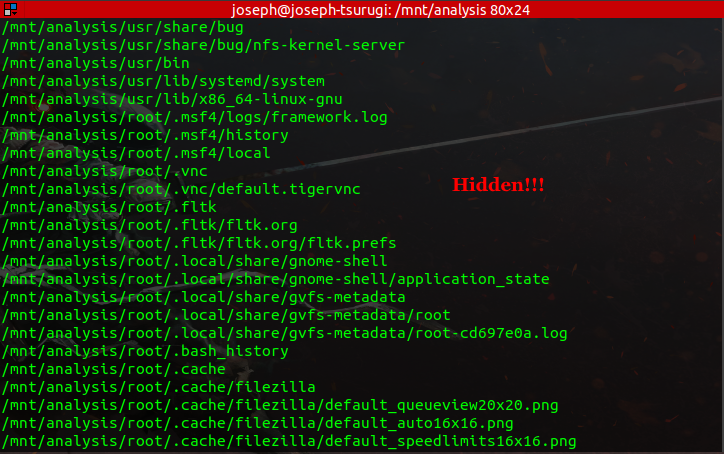
The examination now focuses on the hidden files and directories associated with the Metasploit Framework. Presented below is the content of the concealed directory uncovered during the analysis.

Analysis of the hidden /.msf4/history file yielded critical intelligence. The file disclosed the IP address of the target system, along with detailed records of the various exploits employed by the attacker during the operation. This artifact provides a direct window into the Metasploit Framework’s operational history and the adversary’s exploitation methodology.

The history file further enumerated the specific exploits launched by the attacker against the target system:
- CVE-2011-2523: vsftpd 2.3.4 - Backdoor Command Execution Vulnerability
- CVE-2007-2447: Remote Command Injection Vulnerability - Samba usermap_ script
- CVE-2010-2075: UnrealIRCd 3.2.8.1 Command Execution Vulnerability
- CVE-2010-0094 - Java Runtime Environment Vulnerability
Subsequent review of the /.msf4/logs/framework.log file provided additional context. The output clearly indicates that the attempted exploits were unsuccessful, as evidenced by the failure records and error responses logged during the attack sequence.
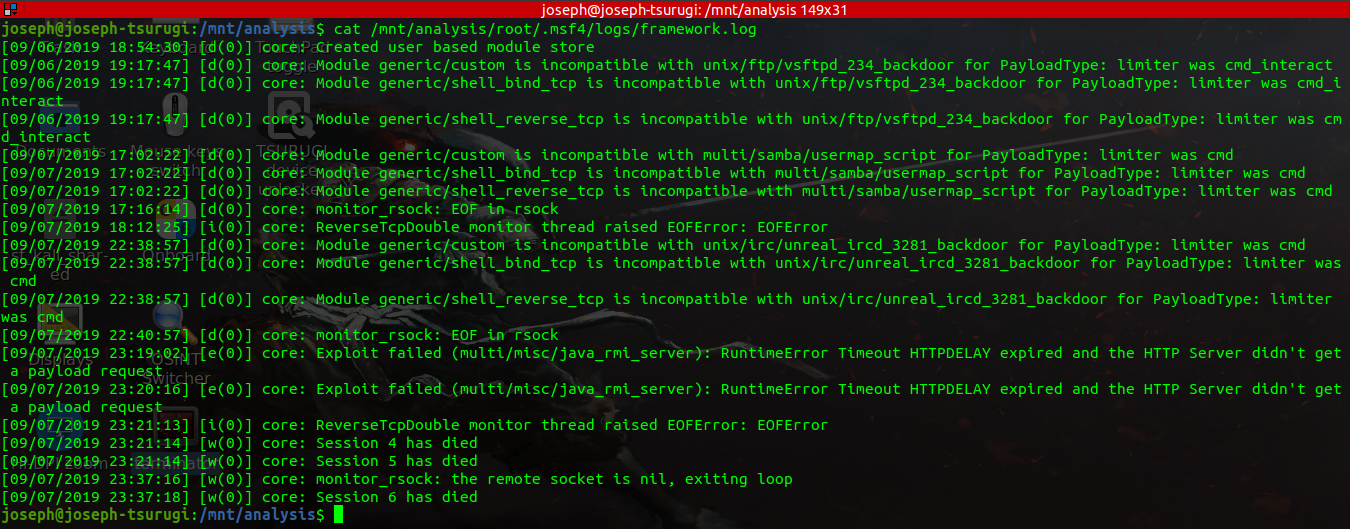
The investigation now turns to the hidden files associated with TigerVNC. Examination of the TigerVNC configuration file disclosed the IP address of the victim’s server, providing further confirmation of the attacker’s remote access targeting and connection details.

The forensic examination now proceeds to the reconstruction of the attacker’s command-line activity and interaction history. This phase focuses on recovering and analyzing the sequence of commands executed by the adversary on the compromised system, providing critical insight into their operational tactics, reconnaissance efforts, and post-exploitation behavior.
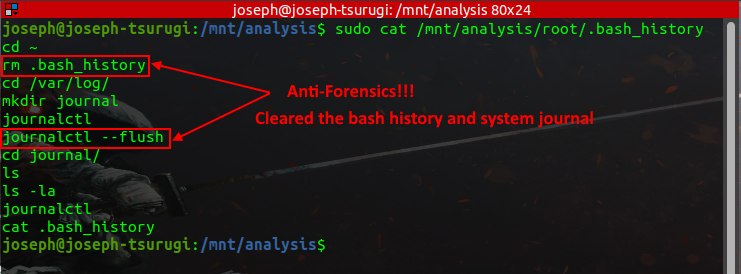
In an apparent attempt to conceal his activities and impede forensic recovery, the attacker cleared both the Bash history and the systemd journal. Nevertheless, residual evidence of his operations persisted within the system, demonstrating that complete eradication of artifacts is exceedingly difficult in a properly configured forensic examination.
Post a Comment